An organisation approves an AI policy.
The principles look sensible.
Human oversight. Transparency. Privacy. Accountability. Fairness. Risk management.
Then somebody deploys an AI agent inside a live business process.
It identifies a customer as high risk. The confidence level is borderline. Two data sources disagree. The customer is commercially important. The decision falls outside the normal case.
Now the organisation needs an answer.
Who decides what happens next?
That question is where AI governance becomes real.
Across Africa, much of the policy architecture around artificial intelligence is beginning to take shape. National strategies have emerged in countries including Kenya, Rwanda, Nigeria, Egypt and others. The African Union has its Continental AI Strategy. Regulatory bodies are increasingly examining how existing privacy, cybersecurity and consumer-protection rules apply to AI.
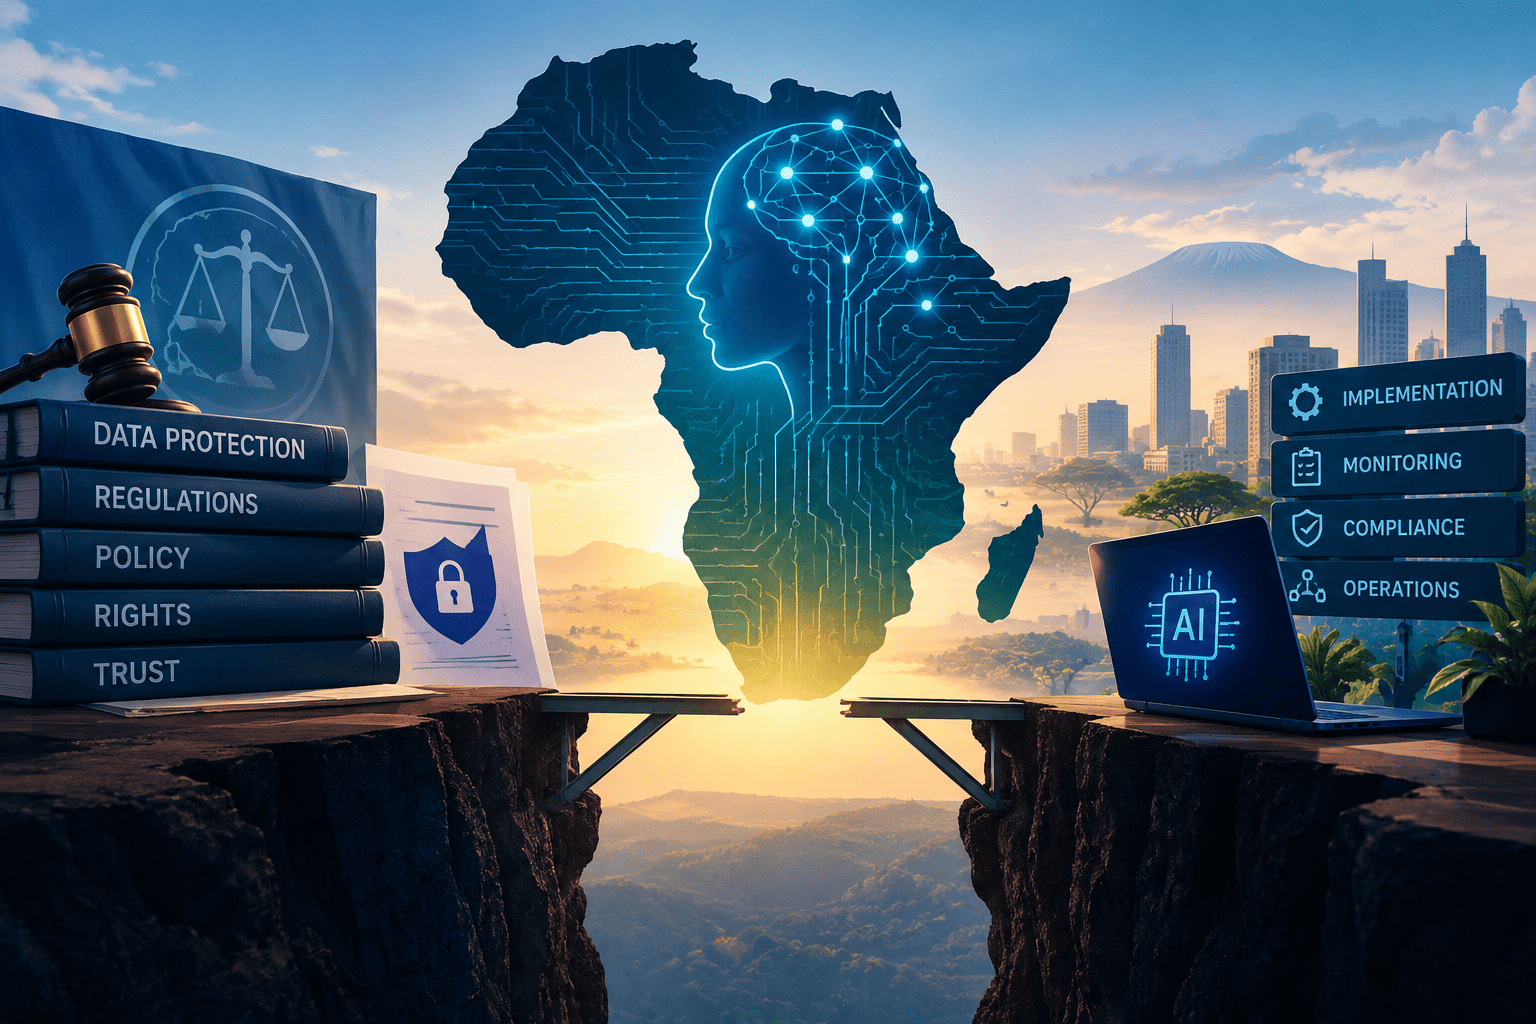
The next challenge is harder: turning those principles into decisions that organisations can actually execute.
The OECD has already identified this implementation gap. Its 2026 work on AI governance in Africa found that countries adopting AI strategies continue to face difficulties translating policy ambitions into effective governance and implementation.
That challenge will increasingly appear inside companies too.
The next phase of African AI governance will therefore be less about writing principles. It will be about designing operating models for decisions.
Table of Contents
- A Principle Does Not Resolve an Exception
- AI Makes Hidden Decision Rights Visible
- Infrastructure Alone Will Not Solve It
- “Human in the Loop” Is Not an Operating Model
- African Organisations Should Govern Decisions by Consequence
- Decision Rights Matter More as AI Becomes Agentic
- Data Governance Sits Underneath AI Governance
- The Exception Path Is Where Governance Becomes Visible
- Governance Needs Service Levels
- This Is Where Minimum Viable Governance Matters
- Africa’s Implementation Opportunity
A Principle Does Not Resolve an Exception
Most governance frameworks describe the normal case reasonably well.
An AI system should use approved data. A human should remain accountable. High-risk decisions require oversight. Personal information should be protected.
But business risk tends to live in the exceptions.
Suppose an AI-powered lending process identifies a customer for rejection. The model is operating within its approved threshold. But one of the underlying attributes has recently failed a data-quality check.
Does the decision continue? Does somebody intervene? Who? What authority do they have? How quickly must the issue be resolved? Can the system use an alternative source? What gets recorded for later review?
A policy saying that decisions require “appropriate human oversight” does not answer those questions. The organisation needs an operating mechanism.
That is the difference between governance as intention and governance as decision infrastructure.
AI Makes Hidden Decision Rights Visible
Many organisations already operate with ambiguous decision rights. They just manage around them.
A business team and IT disagree about a customer definition. Someone senior makes the call. Two departments use different versions of a KPI. Finance reconciles them before the board meeting. A customer falls outside the normal process. An experienced employee knows whom to call.
These arrangements are informal, but they work because people provide context.
AI reduces that flexibility.
A machine cannot rely on organisational memory in the same way. It needs to know which data is authoritative, which thresholds apply, what it is permitted to decide, when it must stop, who receives the escalation, and who has authority to resolve it.
The more autonomous the system becomes, the more explicit those decisions must become.
This is why AI governance quickly becomes an operating-model issue.
Infrastructure Alone Will Not Solve It
Africa is investing in the infrastructure needed to support AI. That is necessary.
UNDP recently examined country-hosted AI compute deployments across Kenya, Malawi, Rwanda, South Africa, Togo and Zambia. Its conclusion is instructive: compute capacity alone is not enough. Effective use depends on usable data, capable people, sustainable financing, cybersecurity, clear institutional responsibilities and governance arrangements around access and value.
The same applies inside enterprises.
An organisation can acquire excellent AI technology. It can secure access to models. It can modernise its cloud environment. It can integrate more data. None of those things determines who can approve an exception when an automated decision becomes ambiguous.
Architecture can enable the decision. It cannot replace the decision.
“Human in the Loop” Is Not an Operating Model
One phrase appears repeatedly in AI governance discussions: human in the loop.
It sounds reassuring.
But which human? With what information? With what authority? Within what timeframe? And responsible for what consequence?
Imagine an AI system flags a payment as suspicious.
If the person reviewing the alert has no authority to release the payment, they are not really the decision-maker. If they can override the system but have no access to the information explaining why the model reached its conclusion, the oversight is weak. If every low-risk exception requires senior approval, the process becomes unworkable. If nobody is clearly responsible, accountability becomes ceremonial.
Human oversight only works when the organisation designs the decision around it. That means defining roles, authority, escalation and evidence. Not simply inserting a person somewhere in the process.
African Organisations Should Govern Decisions by Consequence
One reason AI governance can become bureaucratic is that organisations try to govern every system in the same way.
That rarely makes sense.
An AI tool summarising internal documents is not equivalent to a system deciding whether a customer receives credit. A marketing recommendation is different from changing a medical treatment. A chatbot suggesting a product is different from an autonomous agent initiating a payment.
The governance burden should reflect the consequence.
The first question therefore should not be: Which AI policy applies?
It should be: What happens if this decision is wrong?
From there, organisations can determine the level of control required: how reliable must the underlying data be, how much autonomy can the system have, what evidence must be retained, when is human approval mandatory, how quickly must somebody respond to an exception, can the decision be reversed, and who carries the business consequence.
This is more practical than applying the same governance checklist to every use case.
Decision Rights Matter More as AI Becomes Agentic
The issue becomes even more important with AI agents.
Traditional AI systems often analyse, predict or recommend. Agents can increasingly act. They can query systems, trigger processes, communicate with customers, update records, initiate transactions.
The governance question therefore moves beyond what the AI can access. It becomes what the AI is authorised to decide and do.
I use the term Bounded Autonomy for this. An AI system can operate independently, but only within explicit boundaries. Those boundaries might include a financial limit, an approved customer segment, a defined set of data, a particular business process, a confidence threshold, a list of permitted actions, or specific circumstances requiring human escalation.
The objective is not to remove autonomy. If every action requires approval, much of the value disappears.
The objective is to make autonomy proportional to consequence.
Data Governance Sits Underneath AI Governance
AI governance is sometimes treated as a new discipline detached from existing data governance. Operationally, the two quickly meet.
An AI system cannot reliably make a governed decision if the organisation cannot answer basic questions about the data supporting it. Which source is authoritative? How current is it? What does the field actually mean? Who owns the definition? Can this information legally be used for this purpose? What happens when two systems disagree? Is the data sufficiently reliable for this particular decision?
These are data-governance questions. And they become more important when machines act faster than people can manually reconcile the underlying information.
This does not mean every organisation needs a large enterprise data-governance programme before deploying AI. It means governance should follow the decisions that matter.
If an AI use case relies heavily on customer identity, govern the critical customer data. If it depends on product classifications, establish confidence there. If it makes financial decisions, prioritise the data driving those decisions.
Start with consequence. Then expand.
The Exception Path Is Where Governance Becomes Visible
A useful test of any AI governance framework is not what happens when everything works. Ask what happens when the normal rule fails.
The model confidence falls below the expected threshold. A customer challenges the decision. A required attribute is missing. Two systems disagree. A local regulation conflicts with a group-wide process. The AI recommends an action outside its normal operating range.
Who sees the exception? Who can decide? What evidence do they receive? How quickly must they respond? Can they override the system? Does the override become part of the future learning process?
If an organisation cannot answer those questions, the governance framework is incomplete.
Policies matter. But the exception path is often where accountability becomes visible.
Governance Needs Service Levels
There is another implication that gets little attention.
Governance decisions increasingly need response times.
Traditional governance can tolerate relatively slow processes. A definition is disputed. A stewardship group discusses it next week. A governance council resolves it next month.
That model becomes difficult when AI is embedded in operational processes. A customer may be waiting for an answer. A transaction may be blocked. A supply chain process may have stopped. A risk alert may require immediate action.
Governance therefore needs something similar to service levels. Which issues require resolution within minutes? Which within hours? Which can wait for a monthly forum? Which decisions can be delegated closer to the process? Which require senior authority?
Governance becomes faster when decision rights are distributed intelligently rather than centralised unnecessarily.
This Is Where Minimum Viable Governance Matters
African organisations should resist two extremes.
The first is deploying AI quickly and assuming governance can be added later. The second is trying to build a complete governance framework before allowing experimentation.
Neither is attractive.
A more practical approach is Minimum Viable Governance.
For each meaningful AI use case, identify the minimum set of controls needed to operate responsibly: the critical data, the permitted actions, the decision thresholds, the accountable business owner, the exception process, the escalation authority, the evidence required.
Then operate. Learn. Measure what fails. Strengthen the controls that matter. Expand as the use case expands.
This is governance designed around business reality rather than theoretical completeness.
Africa’s Implementation Opportunity
The World Bank is again encouraging African countries to invest in AI as part of a broader effort to improve productivity and growth. It has also highlighted data protection and shared digital infrastructure as important enablers.
That investment matters.
But Africa’s AI opportunity will not be determined only by access to models or compute. It will also depend on whether organisations can turn governance principles into operational capability.
That means deciding who can make which decisions, what machines are allowed to do, what information they may use, what happens when normal rules break, where humans must intervene, and how quickly governance can respond without stopping the business.
Africa does need good AI policies.
But the next competitive advantage will come from organisations that can operate those policies at the speed of the decisions they govern.
The difficult part of AI governance is no longer writing another principle. It is deciding what happens on Tuesday morning when the machine encounters something nobody expected.
That is where governance becomes real.